



November 11, 2026
|
5 min read



Blazingly fast way to build, track and deploy your models!
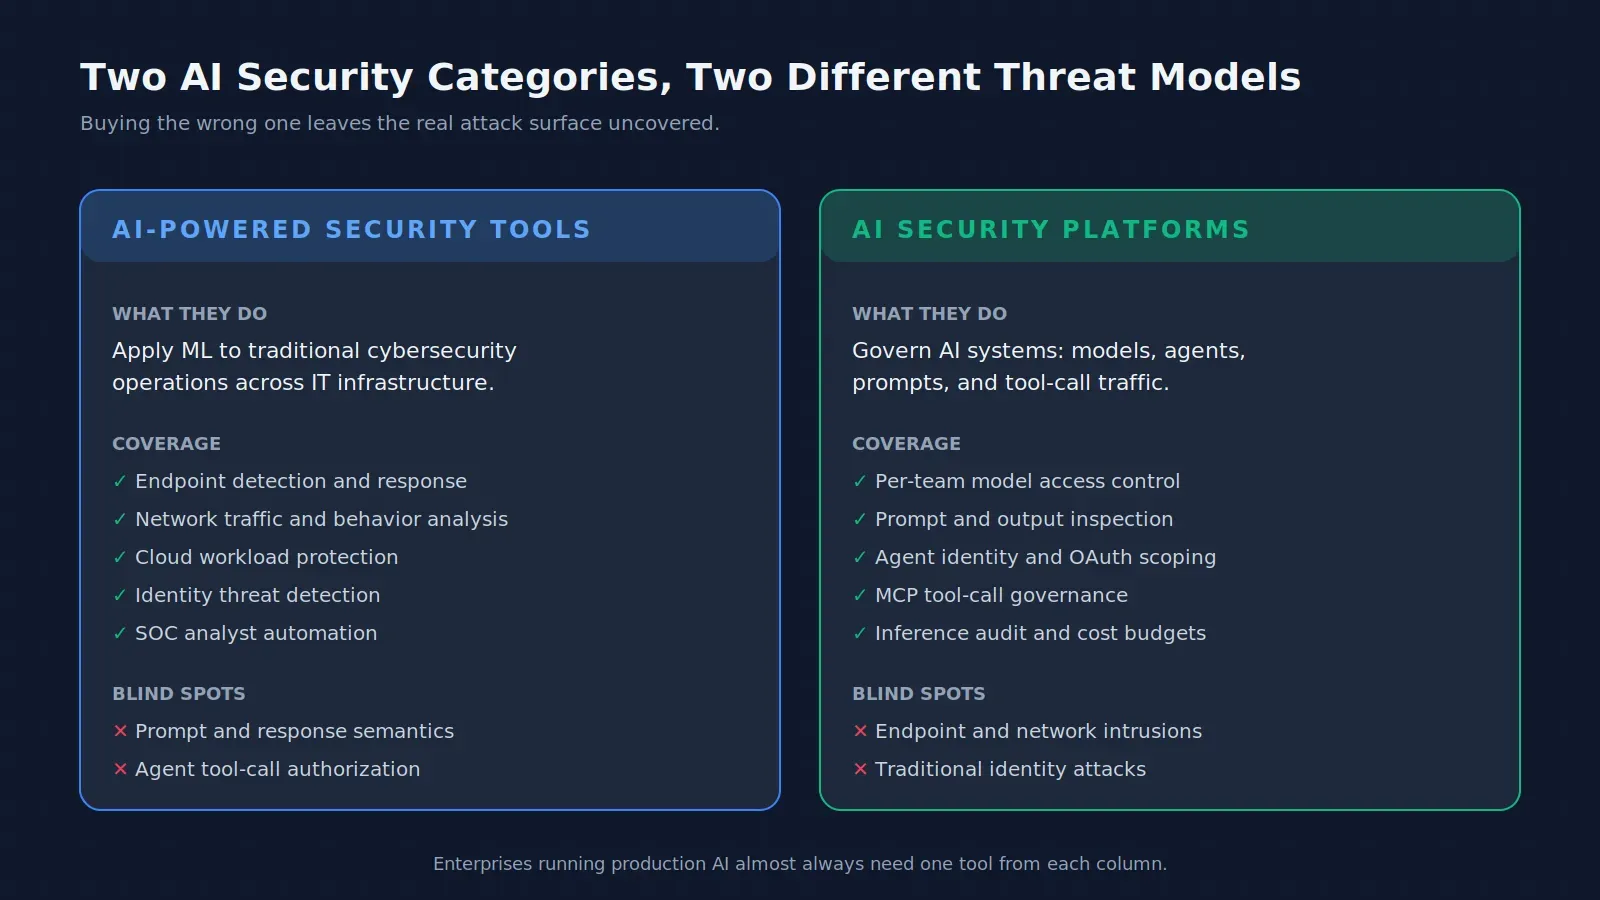
Most evaluations of AI security tools combine two categories that solve different problems. One category uses machine learning and artificial intelligence to strengthen existing cybersecurity workflows across endpoints, networks, identities, and cloud workloads. The other category governs AI systems themselves, including models, prompts, agents, data flows, and tool execution.
This distinction matters for security leaders making buying decisions. A SOC platform with an AI assistant cannot stop an agent from calling a tool it should never touch. A model scanning service cannot cap inference spend, enforce tool-level permissions, or govern model access across production AI applications.
The threat model, deployment pattern, and working definition of secure differ across both categories. Traditional cybersecurity tools improve detection, investigation, and response across IT environments. AI security platforms control the new AI attack surface created by LLMs, agents, MCP servers, prompts, and enterprise data.
This guide separates the market clearly. It compares leading AI security tools, explains where AI security software helps, and shows what both categories miss once autonomous AI agents reach production. You should finish with a buying framework, not a simple vendor ranking.
AI security tools fall into two categories: AI-powered security tools, which use AI to strengthen traditional enterprise security, and AI security platforms, which protect AI models, applications, agents, and their interactions with data and tools. Although both improve security, they address different risks.
Getting the category distinction right matters because both tool types protect different risk surfaces. AI-powered security tools strengthen the cybersecurity stack that enterprises already use. They apply machine learning to endpoint detection, network detection, identity monitoring, threat detection, and SOC triage automation.
These tools are usually owned by security operations, security operations centers, and incident response teams. Their threat model covers malware, phishing, identity compromise, network intrusion, suspicious user behavior, and cloud misconfiguration. They help reduce alert fatigue and allow SOC teams to manage repetitive tasks with stronger context.
AI security platforms solve a different problem. They govern AI workloads themselves, including models, prompts, agents, data flows, and tool execution. They control which users, teams, and agents can call specific models, access sensitive data, or execute MCP tool calls inside production workflows.
Buying one category when the other is required creates serious gaps. A traditional SOC tool cannot fully govern LLM inference, prompt injection, or MCP tool calls. An AI gateway does not replace endpoint protection. Large enterprises running production AI usually need both categories working together.
The common mistake appears in quarterly security reviews. A SOC team chooses a familiar endpoint or XDR platform to “cover AI.” Platform engineering then ships agents into production without runtime governance. Six months later, an incident exposes the gap, and both teams retrofit controls under audit pressure.
The best AI security platforms protect AI systems themselves. The category is younger than traditional cybersecurity, and vendors differ sharply by deployment model, runtime depth, and governance scope. The right choice depends on whether teams are securing models, governing agents, or controlling full inference traffic.
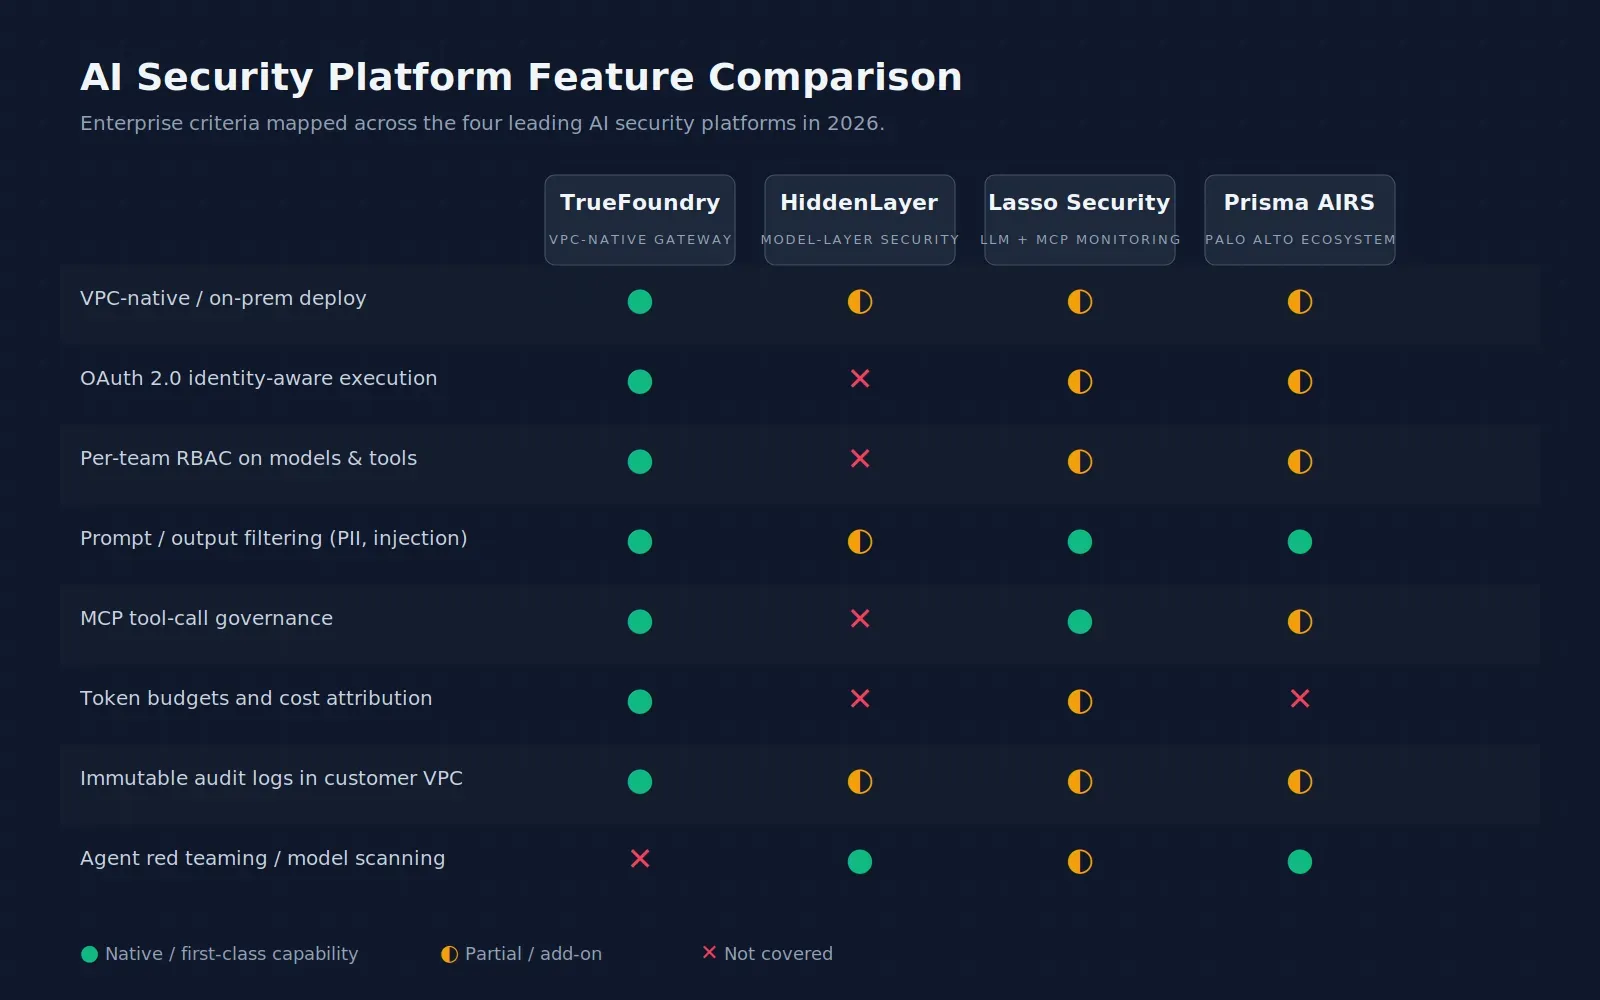
TrueFoundry is an infrastructure-first AI security platform for enterprise AI systems. Its AI gateway centralizes model access, observability, governance, guardrails, and cost controls across enterprise AI workloads. The platform also includes an MCP gateway and an Agent gateway for governing tool-connected and agentic workflows.
TrueFoundry offers three pricing tiers. Developer is free for early experimentation, while Pro starts at $25 per user per month per. Enterprise pricing is custom for organizations needing advanced governance, security, custom deployment, and mission-critical reliability.
TrueFoundry is best for enterprise AI security, platform engineering, AI infrastructure, and compliance teams that need governance across models, agents, MCP tools, and sensitive data workflows. It is especially relevant for organizations running production AI agents, regulated workloads, multi-provider model access, and private-cloud or air-gapped deployments.
HiddenLayer focuses on securing AI models across the AI lifecycle. Its platform supports model scanning, red teaming, AI detection and response, and security posture management. It is strongest when teams need model-layer protection and adversarial AI testing.
HiddenLayer is best for organizations with mature ML development teams that need model-layer protection, scanning, and adversarial robustness testing.
Lasso Security focuses on LLM security, agentic cybersecurity, and MCP protection. Its open-source MCP Gateway acts as a proxy and orchestrator for MCP interactions, adding governance, monitoring, and security controls. It is useful for teams already focused on LLM runtime protection.
Lasso Security is best for organizations prioritizing LLM interaction monitoring, prompt security, and MCP visibility across agentic workloads.
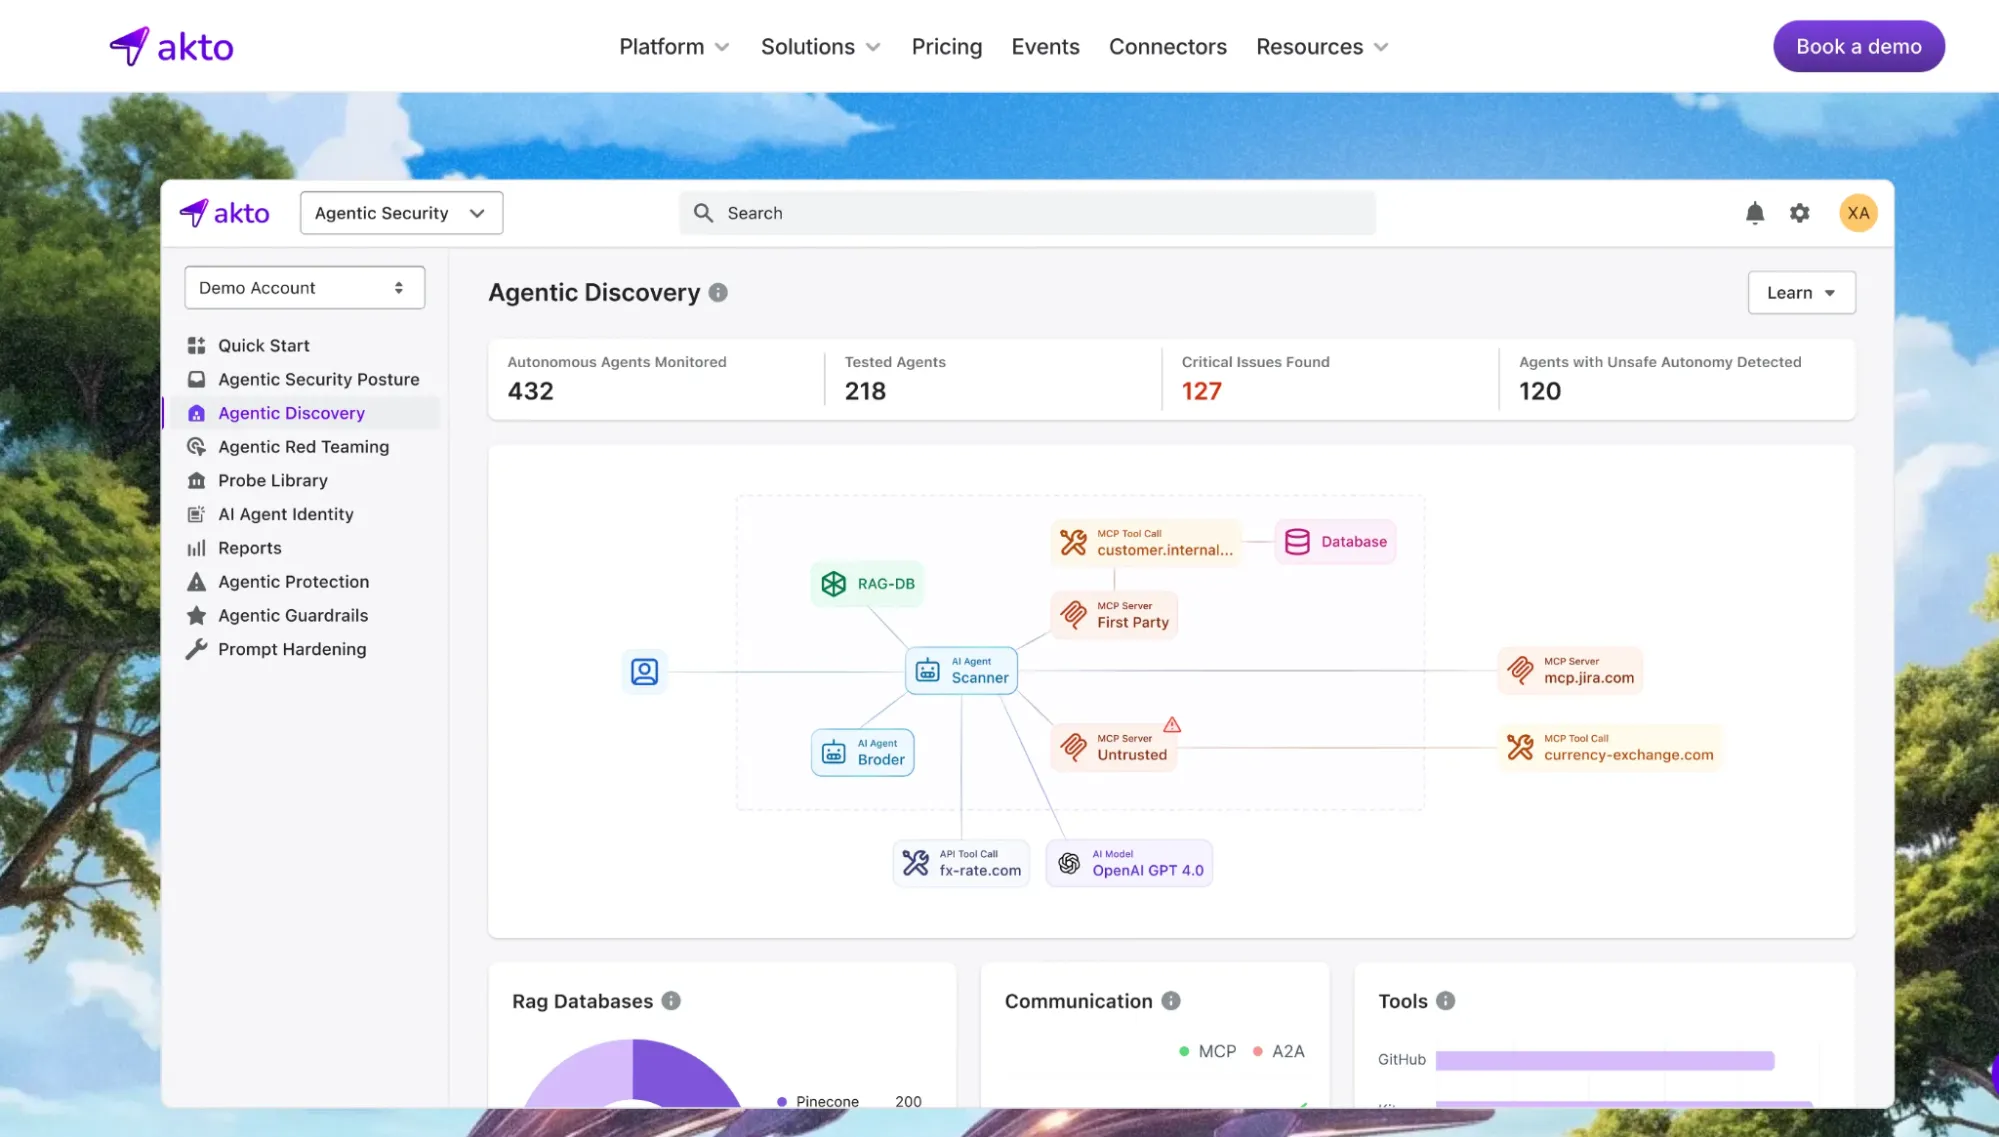
Akto is an AI security platform built to secure AI agents, MCP servers, LLM applications, and the APIs they rely on. It combines AI asset discovery, automated red teaming, runtime guardrails, and AI security posture management to help enterprises identify vulnerabilities and enforce security policies across production AI systems.
Akto is best for enterprises that need to secure production AI applications, AI agents, and MCP servers through continuous security testing, runtime protection, and AI-specific policy enforcement.
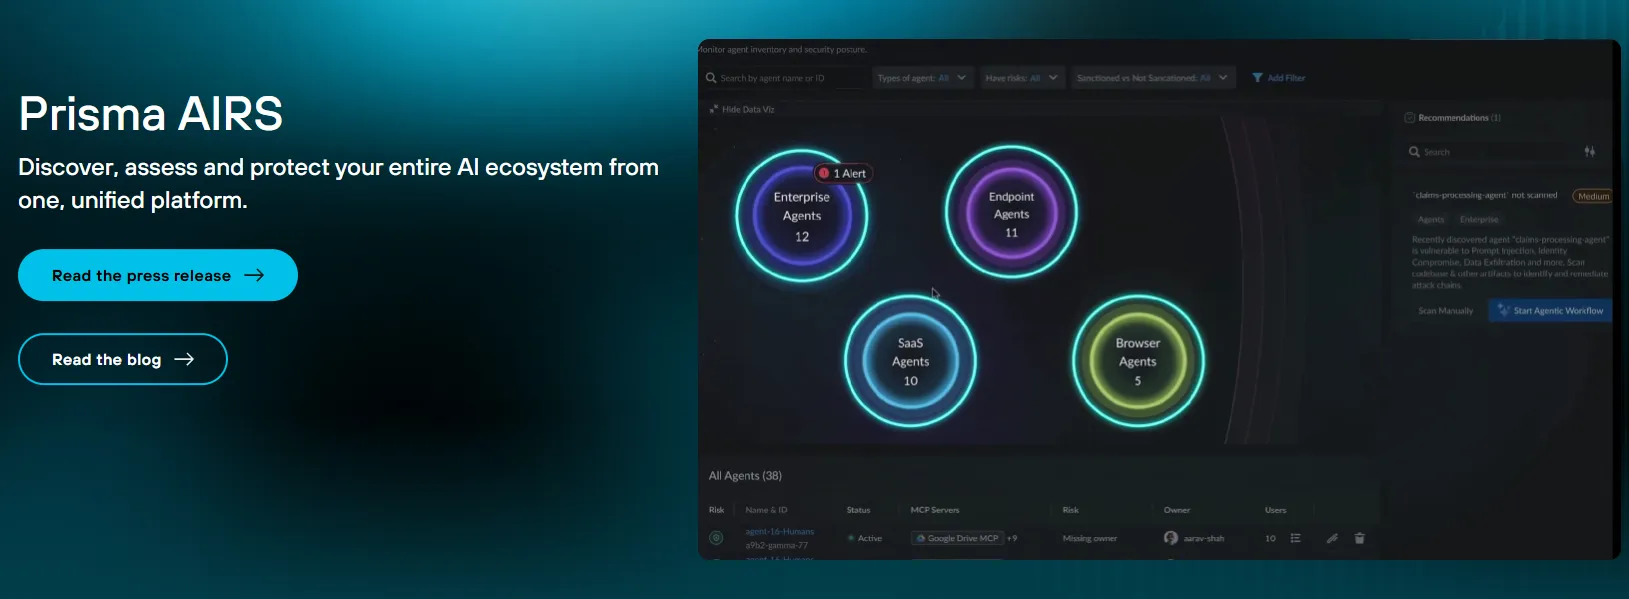
Palo Alto Networks Prisma AIRS is designed to secure enterprise AI applications across the lifecycle. Its capabilities cover AI agents, runtime governance, AI app development, and security assurance. It is most relevant for teams already invested in Palo Alto Networks security architecture.
Prisma AIRS is best for large enterprises already using Palo Alto Networks and seeking AI lifecycle security within that ecosystem.
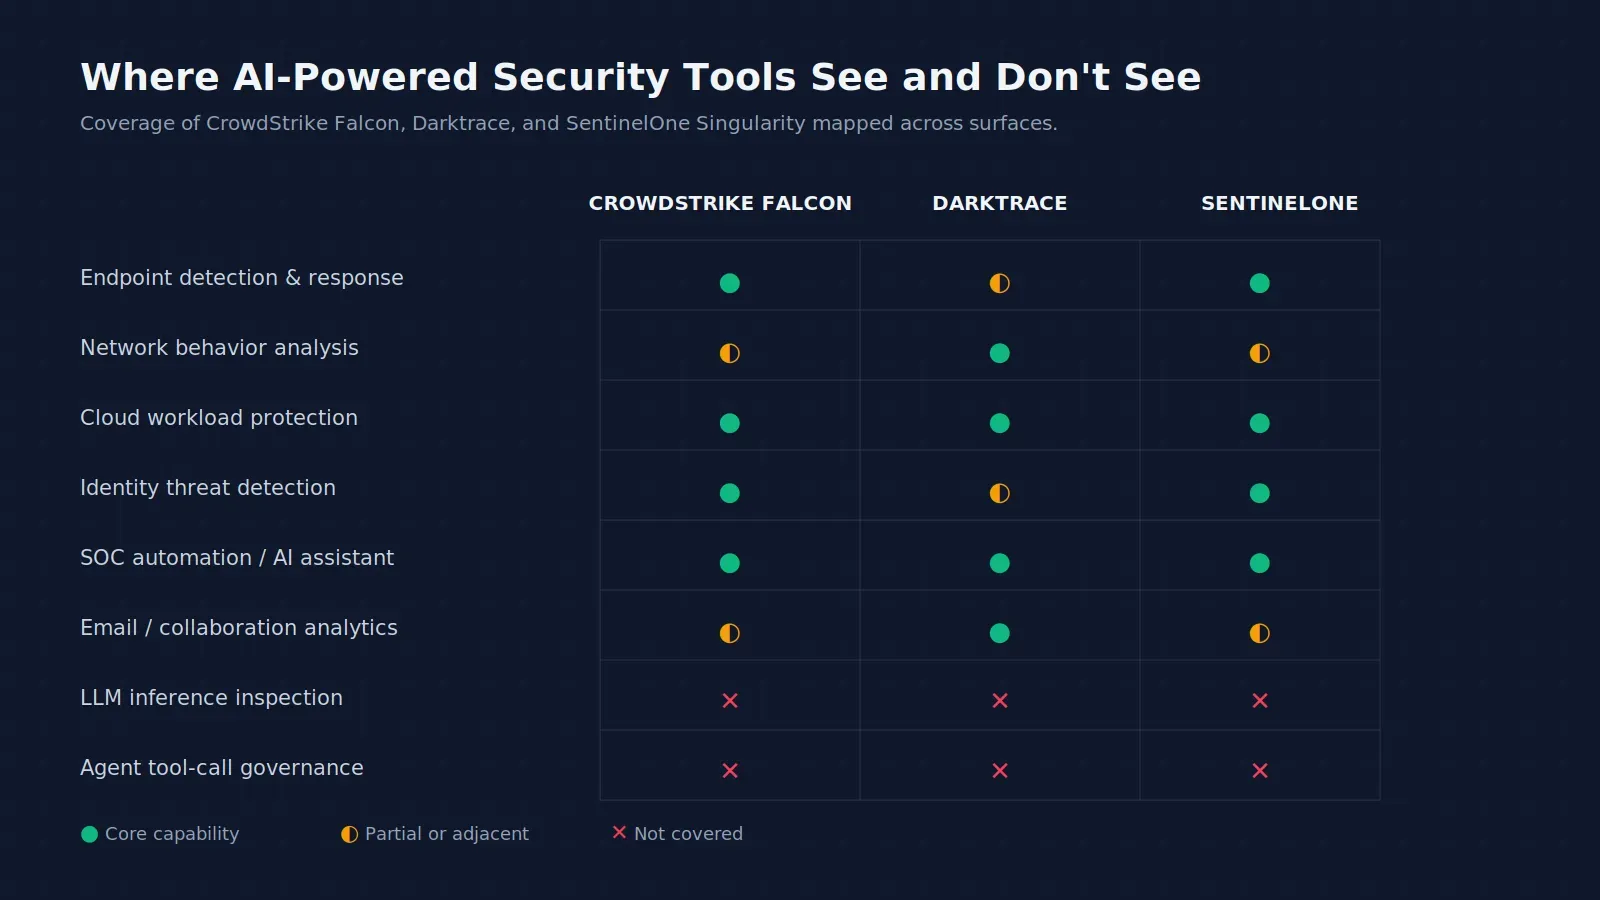
These AI security tools strengthen traditional security operations with machine learning, behavioral analytics, and automated response. They protect endpoints, networks, cloud workloads, and identities, not LLM prompts or agent tool calls.
CrowdStrike Falcon is a cloud-native endpoint and threat intelligence platform for enterprise security teams. It protects endpoints, cloud workloads, identities, and data from one platform. Charlotte AI helps analysts query threats, investigate incidents, and accelerate security operations workflows.
CrowdStrike offers Falcon Go at $7.99 per device per month, Falcon Pro at $14.99, and Falcon Enterprise at $19.99. Falcon Complete pricing is available on request. Check the official pricing page for details.
CrowdStrike Falcon is best for security operations teams that need AI-assisted endpoint, identity, and cloud threat response across large enterprise environments.
Darktrace uses Self-Learning AI to understand normal enterprise activity and identify high-risk anomalous behavior. It supports threat detection across networks, cloud, email, and critical environments. Its strength is real time behavioral analysis across traditional security surfaces.
Darktrace is best for organizations that need AI-driven anomaly detection and real-time visibility across networks, email, cloud, and operational environments.
SentinelOne Singularity unifies endpoint security, identity protection, cloud security, and AI-assisted security workflows. Purple AI helps teams investigate threats, translate data across the security stack, and support analyst decision-making. It is built for autonomous incident response and modern SOC operations.
SentinelOne offers Singularity Complete at $179.99 per endpoint per year and Singularity Commercial at $229.99 per endpoint per year. Singularity Enterprise pricing is available on request. Visit the official pricing page for details.
SentinelOne Singularity is best for SOC teams that need endpoint-to-cloud coverage, AI-assisted investigation, and automated incident response across enterprise environments.
Also Read: Best AI Code Security Tools
AI security tools focus on threats that traditional security controls may not fully detect, particularly those involving prompts, models, agents, data, and AI-connected tools.
Prompt injection: Attackers use carefully crafted instructions to manipulate an AI model into ignoring its original task or revealing information. AI security tools can detect suspicious prompts and apply runtime policies to block malicious requests.
Jailbreaking: Jailbreaking attempts to bypass an AI model’s safety restrictions. Security tools can test models against known jailbreak techniques and apply guardrails to prevent unsafe or restricted outputs.
Sensitive data leakage: AI applications can accidentally expose PII, credentials, business data, or confidential documents through prompts and responses. Security tools help detect, redact, or block sensitive information before it reaches the model or leaves the system.
Data poisoning: Data poisoning involves inserting malicious or misleading data into training or fine-tuning datasets. AI security tools can help identify suspicious data and test models for unexpected behaviour caused by compromised inputs.
Model and API attacks: Attackers can target exposed model endpoints and APIs through unauthorised access, abuse, excessive requests, or crafted inputs. Security tools add authentication, rate limits, monitoring, and runtime controls around these interactions.
Excessive AI agent permissions: Agents with excessive access can potentially read sensitive data or take unauthorised actions. AI security tools can enforce least-privilege access and restrict what an agent can access or execute.
Malicious tool and plugin use: Connected tools, plugins, and MCP servers can introduce new attack paths. AI security platforms can monitor tool calls, control access, and apply policies to prevent agents from using unauthorised or risky tools.
Shadow AI: Shadow AI occurs when employees use unapproved AI applications or models without security oversight. AI security tools help discover this usage, identify associated risks, and bring AI activity under centralised security policies.
The right AI security tool depends on what you are protecting. A traditional enterprise may need endpoint and identity controls, while an AI team may need prompt security, agent governance, or model testing. Match the tool to your AI stack, deployment environment, and security gaps.
If your priority is protecting endpoints, networks, identities, and cloud workloads, start with established enterprise security tools. These provide strong foundational protection but may not offer deep visibility into prompts, model behaviour, or AI agent activity.
Look for tools that can inspect prompts and responses, detect prompt injection and jailbreaks, protect sensitive data, and enforce runtime guardrails. API visibility, model testing, and usage monitoring are also important for production LLM applications.
Agent security requires more than model protection. Look for controls around agent identity, permissions, tool calls, MCP servers, and downstream actions. The tool should help you enforce least privilege and monitor what agents actually do.
Development teams need security earlier in the AI lifecycle. Prioritise model scanning, vulnerability testing, red teaming, dependency checks, and CI/CD integrations that let developers identify issues before an AI application reaches production.
Large organisations need visibility across AI applications, users, models, agents, and data. Look for centralised policies, access controls, audit trails, risk assessment, compliance support, and reporting that security teams can manage across the organisation.
When evaluating an AI security tool, check whether it offers the following capabilities:
Neither category, on its own, provides the guarantees that agentic AI needs in production. AI-powered security tools spot known attack patterns across traditional surfaces. They cannot parse prompt intent, inspect data flows inside AI workflows, or decide whether an agent’s tool call violates business logic.
AI model security platforms protect models during development and runtime. They help with model scanning, red teaming, and threat detection. Yet per-team access control, inference budgets, tool-level gating, and runtime permissions often require a broader control plane.
Data residency creates another gap. If inference traffic routes through a SaaS platform for analysis or governance, proprietary prompts and outputs may leave the organization’s boundary. This matters for regulated teams handling sensitive data, customer records, healthcare data, or confidential enterprise workflows.
Agentic AI needs one enforcement point for models, tools, credentials, and actions. That control plane must bind execution to user identity, retain logs inside the organization’s environment, and enforce policy before execution. Runtime mediation matters more as agents gain access to tools.
A healthcare RAG agent makes the gap clear. An endpoint security tool may never see patient retrieval through an MCP tool. A model-layer scanner may not know whether the requesting user had access rights. The gap closes when the gateway verifies identity, retrieves scopes, and logs the action within the customer VPC.
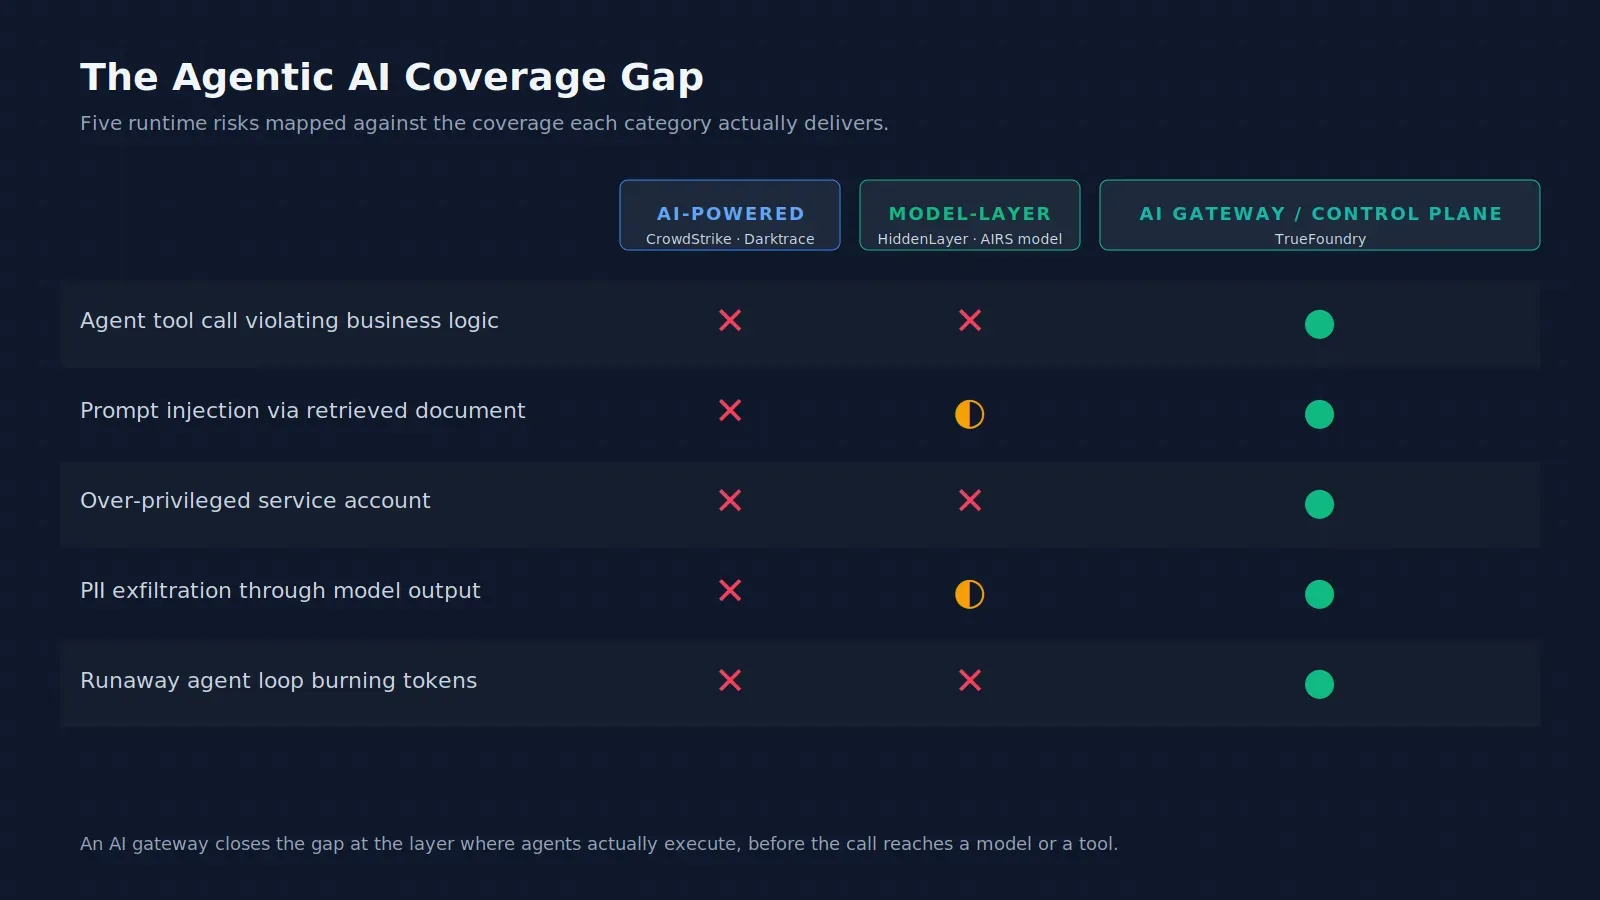
TrueFoundry was built as an infrastructure-first AI security platform for production AI workloads. The AI Gateway deploys inside the customer’s AWS, GCP, Azure, on-premise, or air-gapped environment. It governs AI systems at the layer where model calls, agent actions, and tool requests execute.
Under this model, compliance requirements map to enforceable controls. Identity-aware execution supports least privilege. Prompt filtering supports data handling. VPC-scoped audit logging supports governance evidence. Gateway-level controls turn AI governance from documentation into runtime enforcement.
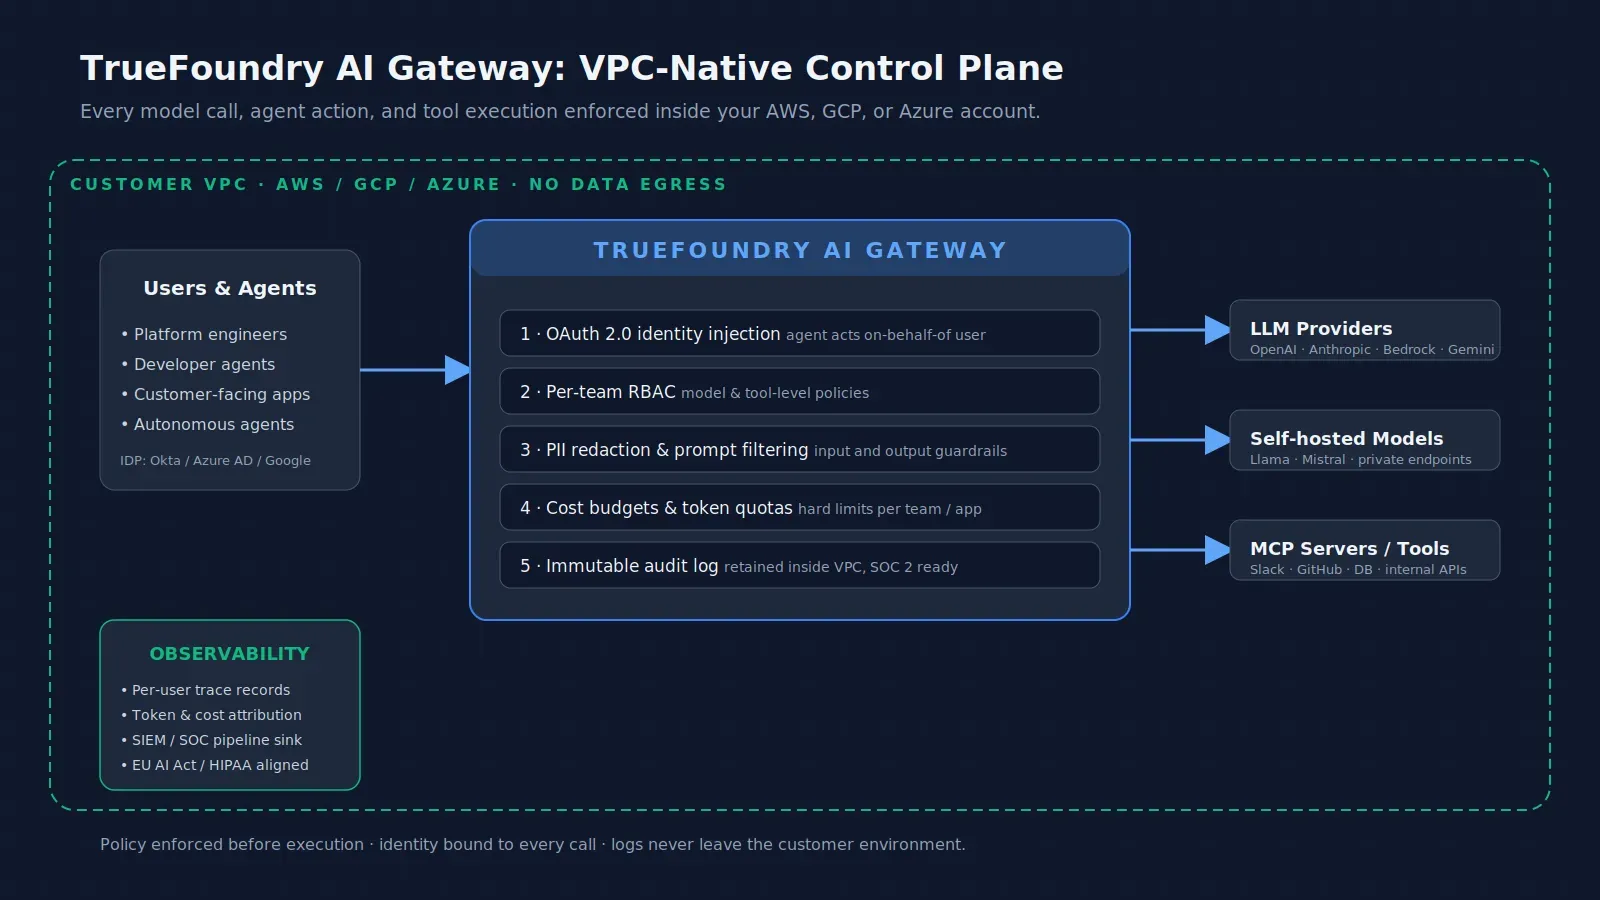
Teams evaluating AI security tools often test two or three categories before seeing the core requirement. Production agentic AI needs a single control plane for models, agents, MCP servers, guardrails, and audit trails.
If your workloads already include autonomous agents calling live systems, walk through the architecture with us before you expand production.
Book a demo with TrueFoundry to map your AI security requirements against a gateway-based reference design.
TrueFoundry AI Gateway delivers ~3–4 ms latency, handles 350+ RPS on 1 vCPU, scales horizontally with ease, and is production-ready, while LiteLLM suffers from high latency, struggles beyond moderate RPS, lacks built-in scaling, and is best for light or prototype workloads.



AI security tools typically address specific risks, such as model scanning, prompt attacks, endpoint protection, or threat detection. AI security platforms provide broader, integrated coverage across models, agents, applications, data, MCP servers, and runtime environments, often combining discovery, testing, governance, monitoring, and protection in one solution.
AI security tools protect enterprise AI systems by identifying vulnerabilities, detecting malicious prompts, monitoring model behaviour, controlling access, and blocking suspicious activity. Depending on the tool, they may also provide vulnerability scanning, red teaming, runtime guardrails, data protection, threat detection, and compliance controls across AI workloads.
Some AI security tools can protect AI agents and MCP servers, but coverage varies significantly. Modern AI-focused platforms may provide agent discovery, tool-call monitoring, runtime guardrails, access controls, and MCP governance. Traditional security tools generally focus on endpoints, networks, or identities rather than agent workflows and MCP interactions.
The three major AI security risks are prompt injection, sensitive data exposure, and excessive or unauthorized agent actions. Prompt injection can manipulate model behaviour, data exposure can leak confidential information through prompts or outputs, and excessive agent permissions can allow AI systems to perform unintended actions.
Five major categories of AI tools include generative AI assistants, AI coding tools, AI analytics platforms, AI automation agents, and AI security tools. Each serves a different purpose, from content generation and software development to data analysis, workflow automation, and protecting AI applications, models, agents, and infrastructure.



The latest news, articles, and resources sent to your inbox













