November 2, 2026
|
5 min read


Blazingly fast way to build, track and deploy your models!
What if your AI system could actually do things: pull data from a CRM, update a dashboard, or send an email, without needing a team of engineers to wire everything up? That's where Model Context Protocol, or MCP, comes in. It's an open standard that helps AI agents securely connect to tools, systems, and data sources with far less effort.
As AI becomes more capable, the real challenge isn't the model, it's giving it access to the right context and actions. MCP solves this with a structured protocol that any tool or agent can speak. If you want to see how this plays out at the infrastructure layer, What is an MCP Gateway builds directly on these foundations. And if you're comparing options for your stack, the best MCP gateways guide covers leading implementations side by side.
So, how does MCP solve the tool-access problem? What does it look like under the hood? And why are companies like Anthropic and Microsoft betting on it? Let's dig in.
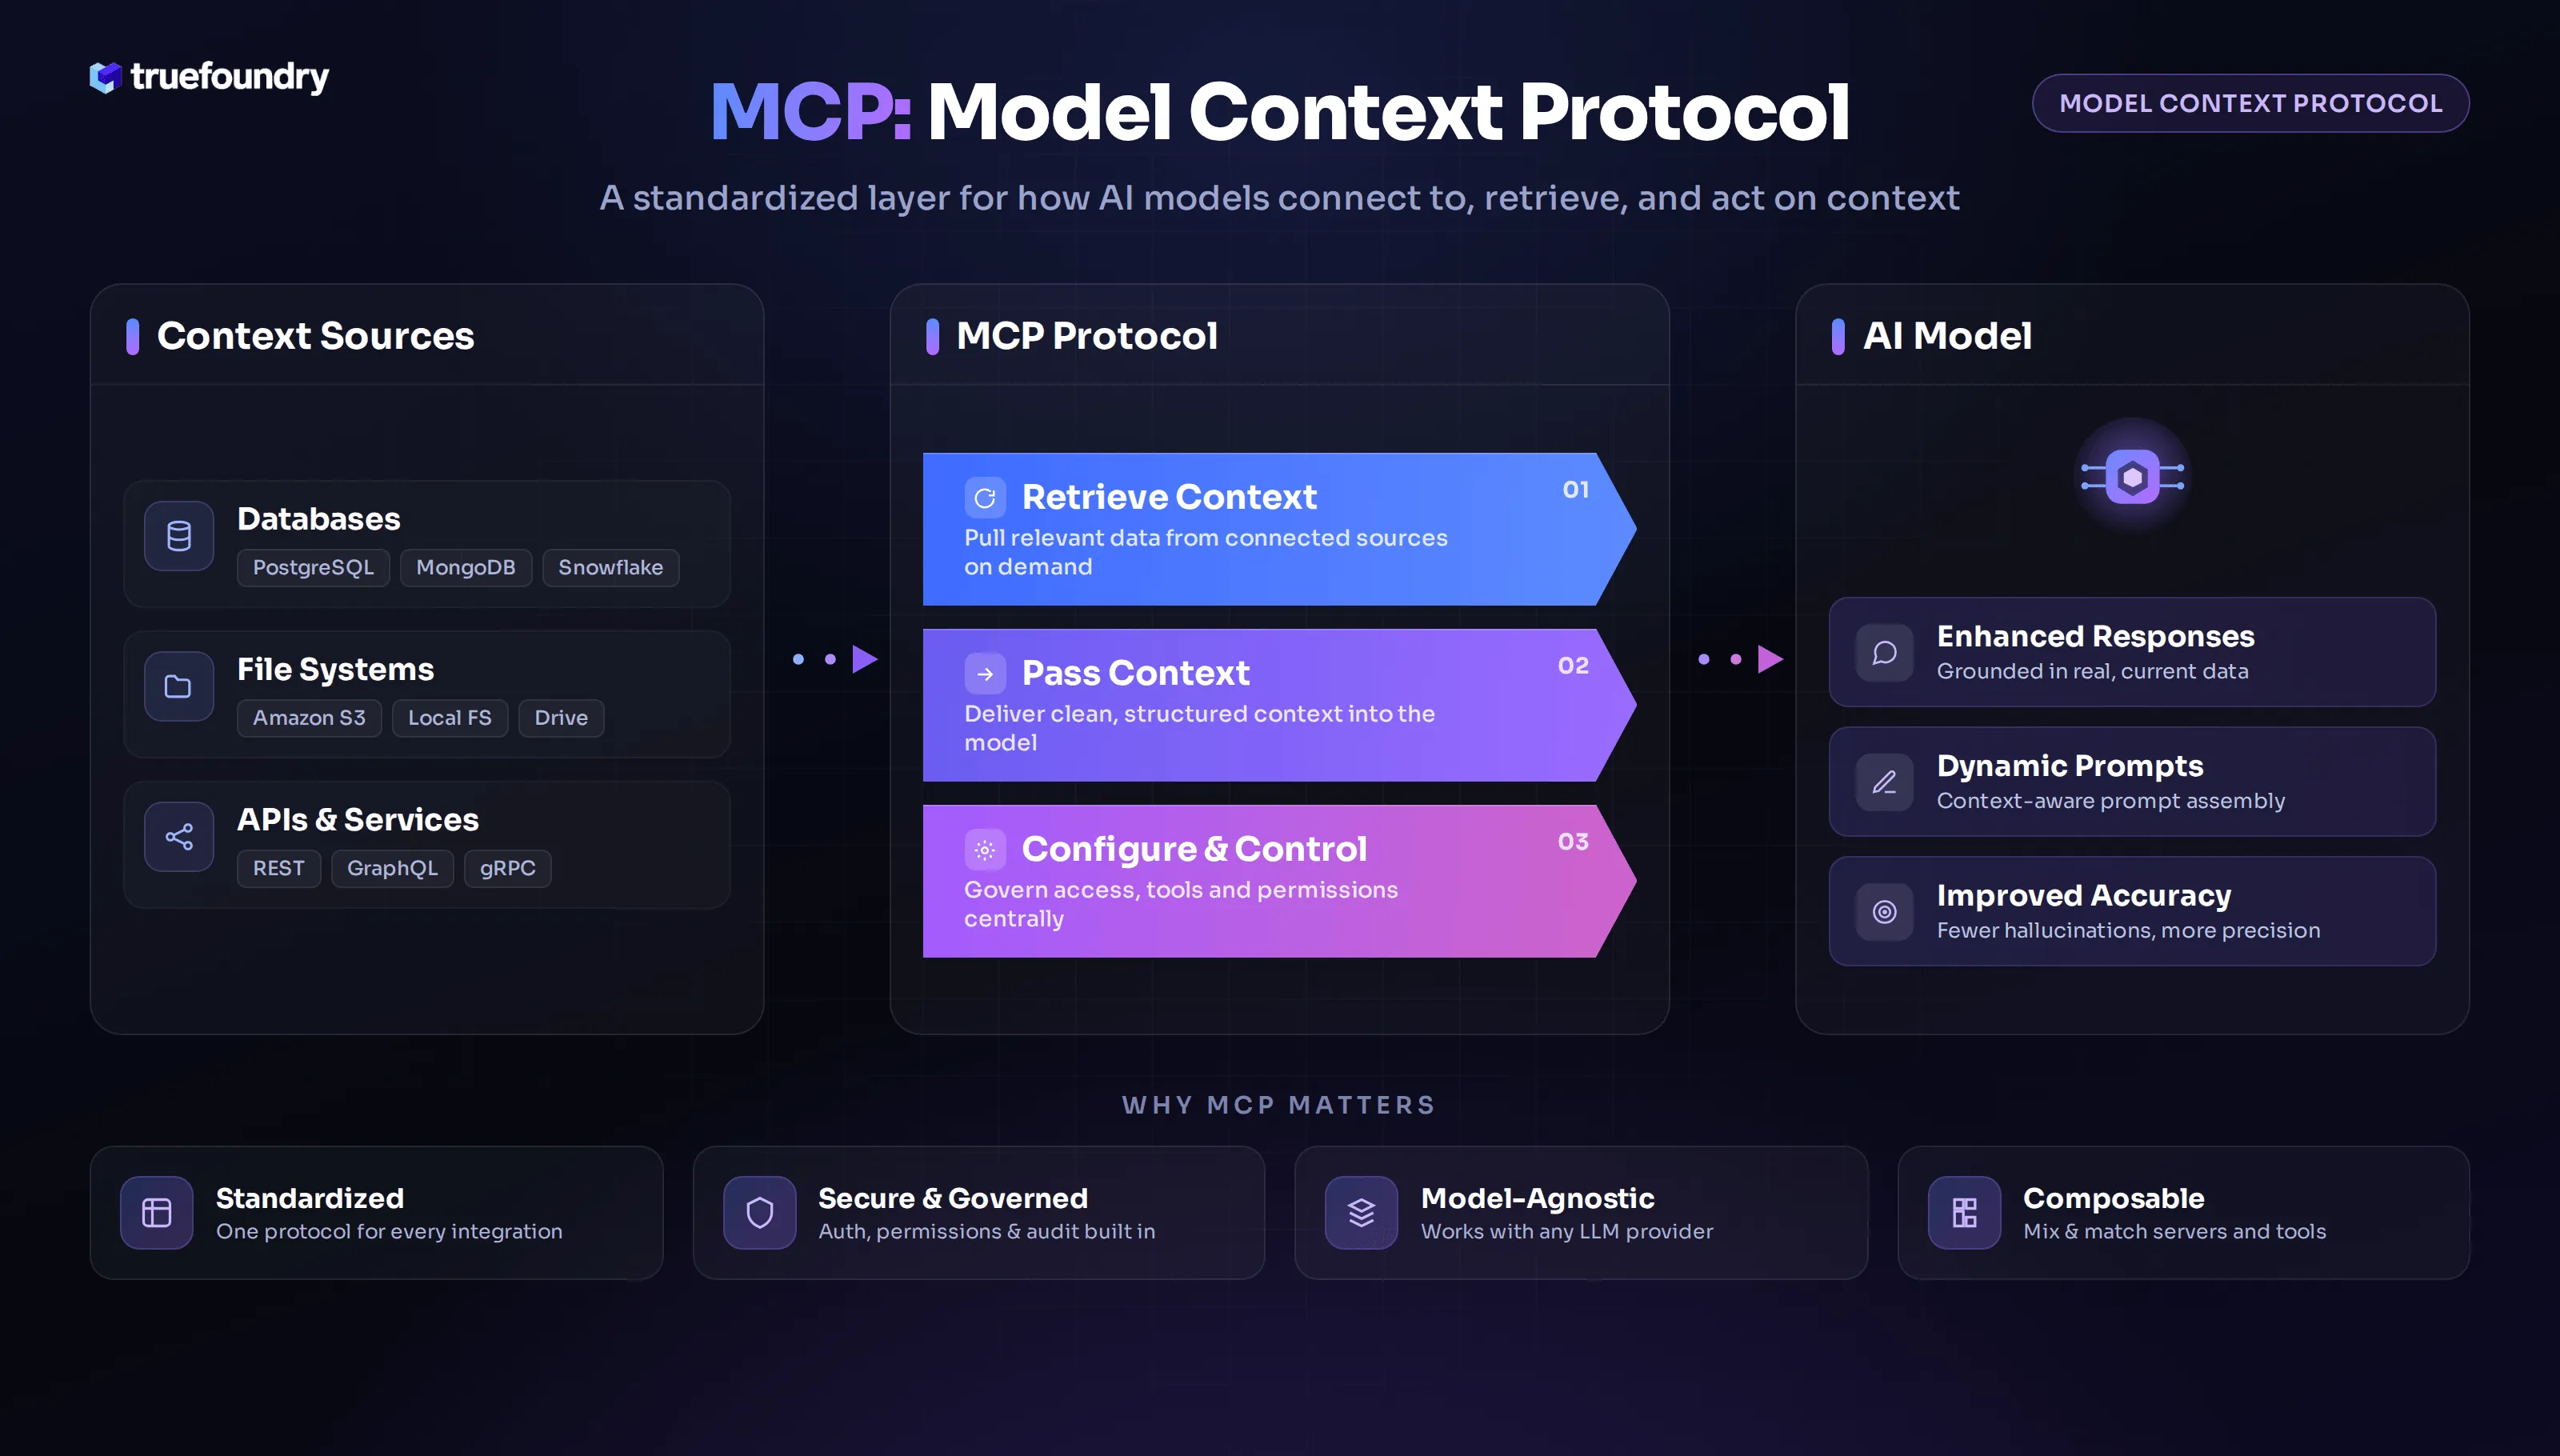
MCP, short for Model Context Protocol, is an open standard designed to help AI agents interact with external tools, data, and services in a structured, secure way. Imagine it like a universal connector that allows your AI model to "plug into" real-world systems, just like a USB port connects devices to your computer. Rather than relying on hardcoded APIs or proprietary integrations, MCP provides a common language for tools and agents to talk to each other. This is the core difference in MCP vs API: traditional APIs expose predefined endpoints, while MCP adds a structured protocol that lets AI systems dynamically discover tools, resources, and prompts at runtime.
The protocol was introduced by Anthropic as part of their broader vision to make AI agents more capable, safe, and autonomous. It uses a simple but powerful architecture: clients (like an AI model) send requests to servers (which wrap tools or data sources), and get structured responses that can be fed back into the model as context.
One of MCP's biggest advantages is that it's modular. Whether your tool is a database, an internal app, a SaaS product, or even a file system, you can expose it as an MCP server. That means your agents don't need to be retrained or re-integrated every time a new system is added, they just follow the protocol.
MCP is also language-agnostic and transport-flexible. It supports multiple SDKs (Python, TypeScript, Java, C#) and can work over different communication layers including HTTP and WebSockets. This makes it easy to use across platforms, whether you're running AI workflows on the cloud, at the edge, or within enterprise IT environments.
At its core, MCP shifts the AI conversation from "what can the model say?" to "what can the model do?" And that's exactly the leap agents need to move from passive assistants to true decision-making collaborators.
As AI agents become more capable, their biggest limitation isn’t reasoning — it’s access. Most language models operate in isolation, without any structured way to interact with external tools or data sources. Developers end up hardcoding API calls, building brittle wrappers, or managing one-off integrations that don’t scale well. This not only slows down development but also introduces security and maintainability issues.
MCP addresses this problem by standardizing how AI agents discover, reason over, and invoke tools. It defines a clean protocol that allows systems to expose their capabilities, such as APIs, databases, or file systems, in a structured, model-friendly way. Agents, in turn, can dynamically learn what actions are available, decide when to use them, and safely trigger them using JSON-RPC.
Consider an AI assistant embedded in an enterprise HR platform. Using MCP, the assistant can connect to a payroll server, an internal knowledge base, and an employee directory, each as an MCP server. When a manager types, “Grant Rahul five days of leave and notify HR,” the model dynamically calls the appropriate tools exposed by these servers: one to update leave status, another to send a Slack message to HR, and a third to log the request in the internal system — all in real time, with zero custom code in the model.
This kind of orchestration would be fragile and expensive to build manually. With MCP, it becomes modular, repeatable, and secure across MCP automation platforms. With MCP, it becomes modular, repeatable, and secure. As organizations deploy more tools and services, MCP ensures AI agents can interact with them safely and intelligently, without needing new integrations for every change.
Model Context Protocol is designed to enable AI agents to securely interact with external tools and data sources using a standardized interface. Its architecture separates responsibilities clearly across three layers: the host, the client, and the server. Each layer plays a specific role in managing access, maintaining isolation, and enabling context exchange.
At the center of it all is a structured, stateful communication protocol built on JSON-RPC 2.0 that handles request-response flows between agents and tool interfaces. The result is a modular system that allows developers to build once and scale across agents, tools, and domains without re-implementation. The architecture supports both local and distributed deployments.
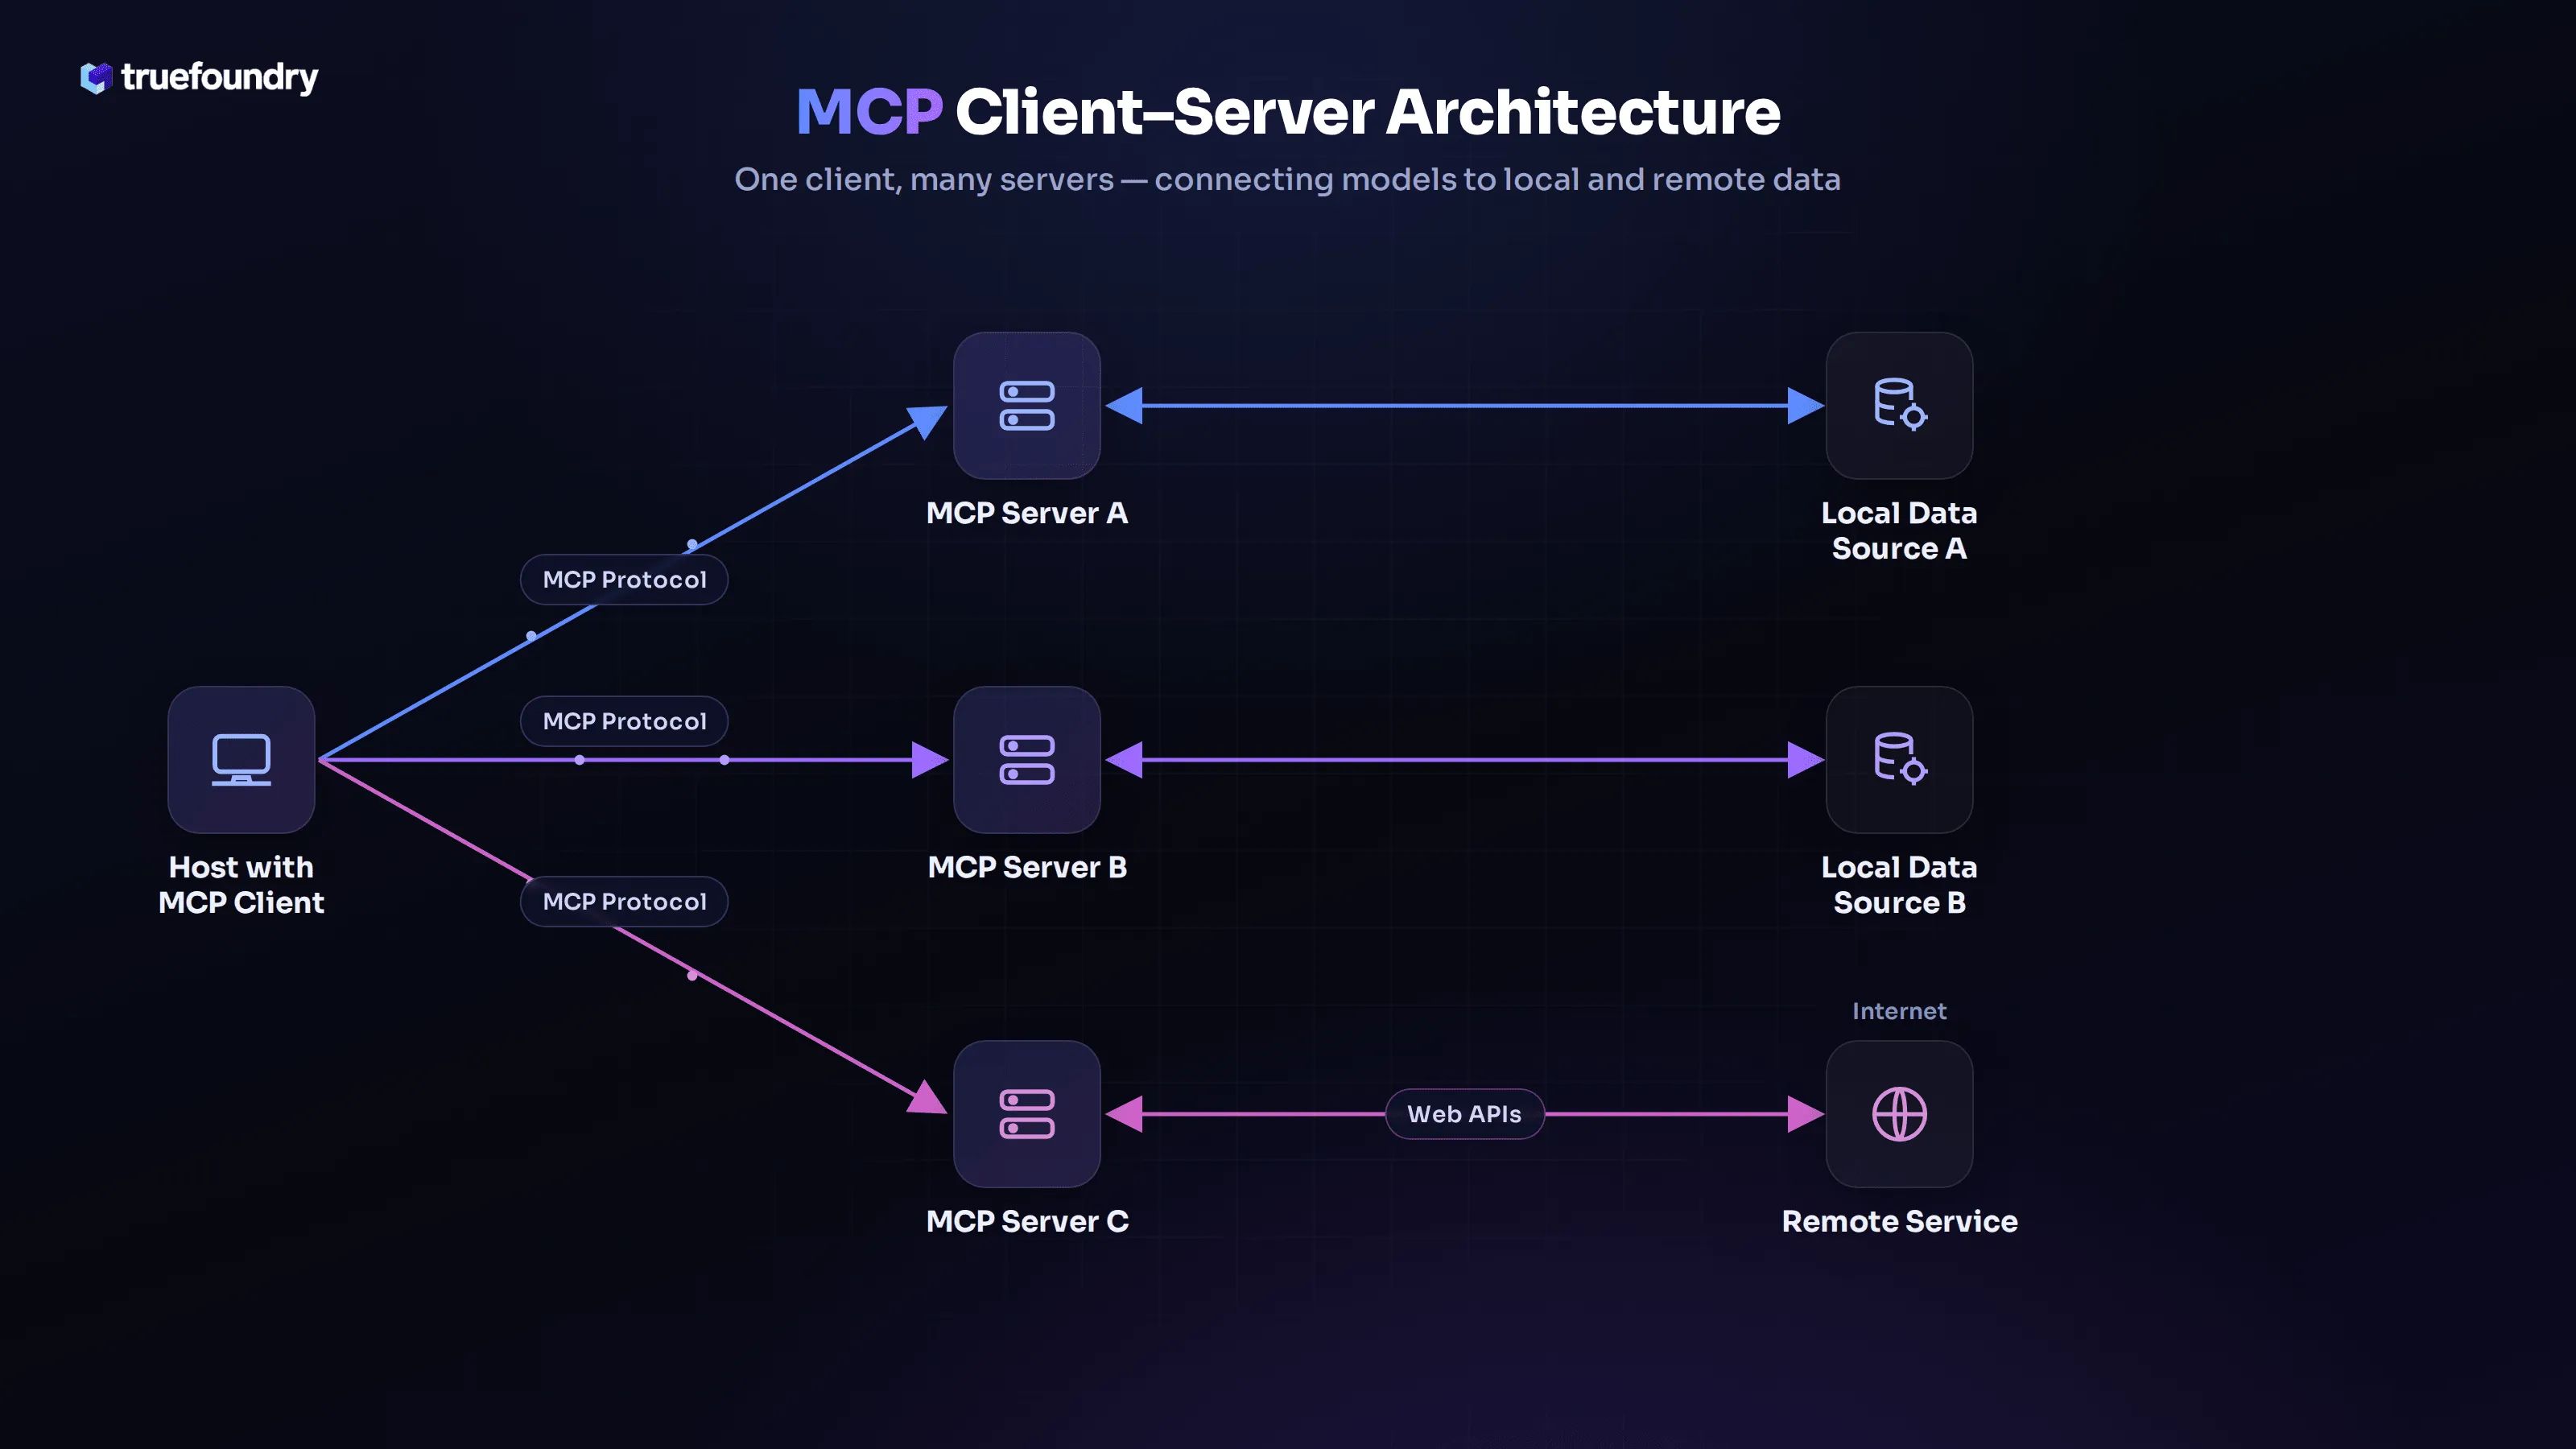
The host is the primary execution environment for the AI agent or model. It coordinates everything from security policies and sampling strategy to tool invocation workflows. Hosts are responsible for spawning and managing client instances and play a central role in how an AI application interacts with the MCP ecosystem.
Hosts enforce access control, user consent, and session boundaries across tools. They handle context aggregation and determine how data from multiple clients is merged and passed to the model.
For example, in a system like Claude Desktop, the host manages several client connections, each one interacting with a different external service, while maintaining a unified context for the model's reasoning loop.
Each client is a dedicated communication bridge between the host and a single MCP server. It negotiates capabilities with the server, manages the RPC session, and routes data back and forth. Clients are designed to be isolated and stateless beyond the scope of a single session.
One client connects to one server, preserving strict isolation and minimizing risk. Clients manage discovery (tools, resources, prompts) and enforce message validation and type safety.
Clients act as the abstraction layer that allows the AI model to invoke tools or fetch data without being directly coupled to the system's implementation details.
An MCP server is a wrapper around an external tool, API, or system. It exposes functionality and data in a standardized format, making it accessible to any MCP-compatible client. Servers operate independently and are responsible for defining their scope of capabilities.
Servers expose three core primitives: tools (actions), resources (data), and prompts (templated flows). They respect access constraints and may be deployed locally or over the network, depending on system architecture.
For example, a server might expose a Postgres database as a queryable resource or wrap GitHub's API as a set of callable tools. Once built, the same server can serve multiple client types across different hosts.
Note: MCP's host-client-server design enforces strict separation of responsibilities. The host controls access and context, each client maintains an isolated session, and servers expose tool capabilities through a standard protocol. This structure is critical for building secure, modular, and scalable AI-agent systems across varied toolchains.
MCP interactions are driven by four key primitives: tools, resources, prompts, and the session layer. These components abstract away low-level complexity and provide a clean interface for models to reason, act, and interact with real-world systems in a modular and predictable way.
Tools are executable functions exposed by the server and callable by the model via the client. Each tool is defined with input parameters, output schema, and a description of its purpose. This metadata is used by the model to determine when and how to use a tool. Examples include creating support tickets, sending Slack messages, or initiating workflows. Tools may be synchronous or asynchronous depending on the backend implementation. The model decides tool invocation timing based on current context and task intent.
Resources are read-only data that servers expose to provide context to the model. These could be database records, documents, log entries, or search results. Clients request resources when the model needs to look up or retrieve data before taking an action. Servers define what is available, and the client handles formatting it for inclusion in the model's prompt. Resources are critical for grounding agent responses in up-to-date and relevant information.
Prompts are predefined templates or interaction flows registered by the server. They serve as structured scaffolds that can guide the model's behavior in specific contexts. For instance, a prompt might define the layout for a bug report, escalation email, or onboarding guide. Prompts can be triggered by the user or invoked programmatically. Their role is to enforce consistency, reduce hallucination, and accelerate structured generation in high-stakes workflows.
All communication between clients and servers happens over JSON-RPC 2.0. This protocol supports stateful, bidirectional messaging and is transport-flexible. It works over STDIO, HTTP/SSE, or WebSockets. The session layer enables request-response calls, event notifications, capability registration, and long-running operations. By adhering to JSON-RPC, MCP ensures strong typing, predictable communication patterns, and compatibility across languages and platforms. This session model is what makes dynamic tool discovery and runtime interaction possible.
Note: Tools, resources, prompts, and the session layer form the foundation of every MCP interaction. They allow models to reason, act, and retrieve context using structured, predictable primitives, enabling real-time integration with external systems without sacrificing safety or flexibility.
MCP simplifies how AI applications connect with external tools and data sources. Its key benefits include standardized integrations, reusable connections, and access to relevant context.
MCP provides a common protocol for connecting AI applications to external tools, APIs, and data sources. Instead of building a separate integration for every AI application, developers can use compatible MCP servers to connect models with services through a consistent interface.
MCP lets developers build tools and integrations once and reuse them across compatible AI applications. For example, an MCP server for GitHub can expose repository search, issue management, and pull request operations to multiple AI clients without requiring a separate integration for each client.
MCP enables AI applications to access relevant information from external sources, including databases, files, and business applications. This gives models more context to answer questions or perform tasks using available information, rather than relying only on knowledge learned during training.
MCP operates through a structured five-step flow that enables large language models to discover, invoke, and interact with tools and data sources in real time. Here's how the protocol works under the hood:
The host application starts the process by launching one or more MCP clients, each configured to connect to a specific MCP server. The host is also responsible for managing user authorization, enforcing access control policies, and maintaining context across multiple tool interactions.
Each client initiates a handshake with its assigned server. During this exchange, the server advertises its supported tools, resources, and prompts, complete with descriptions, input parameters, and return types. The client then packages this metadata into the model’s context so the model knows what it can use.
With capability data now embedded in its prompt, the model reasons over the available tools and current user input. If the task requires action or information retrieval, the model decides which tool or resource to invoke, formulates the appropriate parameters, and sends the request to the client.
The client forwards the model’s request to the server using JSON-RPC. The server executes the function or fetches the data, then returns a structured response. The client delivers the result back to the model, which uses it to continue processing or make further decisions.
The host application monitors the full loop, managing ongoing session state, logging tool usage, enforcing rate limits, and ensuring the agent stays within its scope. This step ensures safety, traceability, and observability of AI-driven actions.

This diagram shows how an AI agent uses MCP to discover tools, invoke actions, and handle tickets across multiple servers in real time. It visualizes the full end-to-end flow from user input to system response.
Consider an AI support agent embedded in a helpdesk application. When the host application starts, it initializes two MCP clients: one connected to a Zendesk MCP server and another linked to an internal escalation system. Each client performs a capability handshake with its respective server. The Zendesk server advertises tools such as getTicketById and updateTicketStatus, while the escalation server exposes escalateTicket.
This metadata is passed into the model’s context. When a user types the instruction, “Escalate ticket #1289 if it’s marked urgent,” the model interprets the request and determines that it needs to fetch the ticket first. It calls getTicketById("1289") via the Zendesk client. The server responds with the ticket details, indicating the priority is “urgent.” Based on that, the model decides to escalate the issue and calls escalateTicket("1289") through the second client.
Both calls are executed over JSON-RPC. The clients forward the requests to their respective servers, which process the functions and return structured responses. These responses, ticket metadata, and escalation confirmation are routed back to the model and incorporated into its context. The host then finalizes the loop by logging the interactions, validating access policies, and updating the UI with the output: “Ticket #1289 escalated successfully.”
MCP, APIs, and function calling serve different roles in connecting AI applications to external systems. Understanding how they work together helps you decide when to use MCP and when a direct API integration or function calling is enough.
An API defines how applications communicate with a service, such as retrieving customer data or creating a support ticket. MCP provides a standardized way for AI applications to discover and interact with tools and context exposed by an MCP server.
For example, an MCP server can expose a CRM's existing API as tools that an AI assistant can discover and use. You don't need to replace the underlying API; MCP provides an AI-friendly integration layer.
Function calling allows an AI model to request an action by generating a structured function name and its arguments. Your application then executes that function and returns the result to the model.
MCP addresses a different problem: it standardizes how tools are exposed, discovered, and invoked across compatible AI applications. Instead of implementing and maintaining every tool integration separately, developers can expose capabilities through an MCP server and reuse them across clients. MCP and function calling can work together in the same workflow
Before integrating AI systems, it’s important to understand how MCP (Model Context Protocol) and RAG (Retrieval-Augmented Generation) serve different purposes. While both enhance LLM functionality, MCP focuses on connecting models to tools and APIs, whereas RAG enriches model responses with external knowledge.
Connecting an MCP server to an AI application involves configuring the client, establishing a connection, and discovering the tools the server provides. The exact setup depends on your AI client and whether the server runs locally or remotely.
First, configure your AI application to use an MCP client that supports the required transport and authentication method. Add the server connection details, such as the command and arguments for a local server or the endpoint URL for a remote server. Set up any required credentials securely.
The MCP client establishes a connection with the server using a supported transport, such as standard input/output (stdio) for local processes or Streamable HTTP for remote connections. The client and server negotiate protocol capabilities and establish how they will exchange messages. Remote servers may also require authentication before granting access.
Once connected, the client can request the list of tools the MCP server exposes, including their names, descriptions, and input schemas. The AI application can use this information to determine which tools are relevant to a task. When a tool is selected, the client sends a tool-call request to the server, which executes it and returns the result to the application.
Function calling made it possible for language models to interact with tools in a structured way. You define a tool, its parameters, and its purpose, and the model can invoke it by returning a JSON object. This works well for simple use cases, especially when the number of tools is small and static. But function calling has critical limitations: it assumes you know all tools up front, that each model is tightly coupled to them, and that the infrastructure around them is either hardcoded or fragile.
MCP addresses these gaps by introducing a full-fledged protocol, not just a format. For teams evaluating MCP vs A2A, this distinction matters because MCP standardizes model-to-tool interaction, while A2A focuses on communication between autonomous agents. It formalizes the interaction between AI agents and external systems using a host–client–server architecture and structured communication over JSON-RPC. Rather than embedding tool definitions directly into the model’s prompt, MCP allows models to dynamically discover what tools are available at runtime, invoke them securely, and receive structured responses, all through a standard interface.
Imagine an AI assistant embedded inside a retail operations dashboard. With function calling, the model would need to be manually configured with access to tools like getInventory, updatePrice, and notifyWarehouse. Every tool must be hardwired into the agent’s system prompt. But with MCP, you can connect to different servers — one for inventory, one for pricing, one for logistics, and the agent will discover all exposed tools automatically. No hardcoding, no redeploying.
Function calling was a necessary first step. MCP builds on that foundation with the infrastructure, protocol, and flexibility needed for building robust, production-grade agent systems.
MCP connects AI applications to external tools, data sources, and services, but these connections introduce security risks if access is not properly controlled. Securing an MCP implementation requires validating tool outputs, protecting credentials, limiting permissions, and monitoring activity across the client, server, and connected services.
MCP tools and resources can return untrusted content, including instructions designed to manipulate an AI model. If the model follows malicious instructions embedded in retrieved data or tool responses, it could expose sensitive information or trigger unintended actions.
Validate tool outputs, treat external content as untrusted input, and use guardrails to prevent retrieved instructions from overriding application policies. Apply additional checks before sensitive or irreversible operations.
MCP servers may connect to APIs, databases, and business applications using credentials or access tokens. Poor credential handling can expose these secrets or allow unauthorized clients to invoke tools.
Use appropriate authentication for the deployment, such as OAuth-based authorization for remote servers where supported. Store secrets securely, avoid hardcoding credentials, validate access tokens, and apply least-privilege access to limit what each user or client can do.
A tool that can read a file presents a different risk from one that can delete records, transfer data, or modify production systems. Granting broad permissions to every tool increases the impact of compromised clients or unsafe model decisions.
Expose only the tools and operations an application needs. Enforce authorization at the server or connected service, and require human approval for high-impact or irreversible actions. Do not rely on the model alone to enforce permissions.
Production security requires controls across authentication, network access, request handling, and monitoring. Use the following safeguards to reduce the risk of unauthorized access, service abuse, and sensitive data exposure.
Security controls should be enforced by the MCP server, host application, and connected services, not delegated entirely to the AI model. Review permissions regularly, monitor suspicious tool activity, and test the implementation before deploying changes to production.

TrueFoundry’s MCP Gateway provides a single portal to discover and register all your MCP Servers, whether internal, on-premises, hybrid, or third-party, under organized “MCP Server Groups” that isolate environments (for example, dev versus prod) and enforce RBAC-driven approval flows for governance and visibility. Out-of-the-box, the Gateway includes prebuilt connectors for enterprise tools such as Slack, Confluence, Datadog, Sentry, and GitHub, enabling zero-code integration into LLM agent workflows. For custom needs, you can register any internal or proprietary API in minutes to make it instantly discoverable and usable by LLM-powered agents without modifying your SDK.
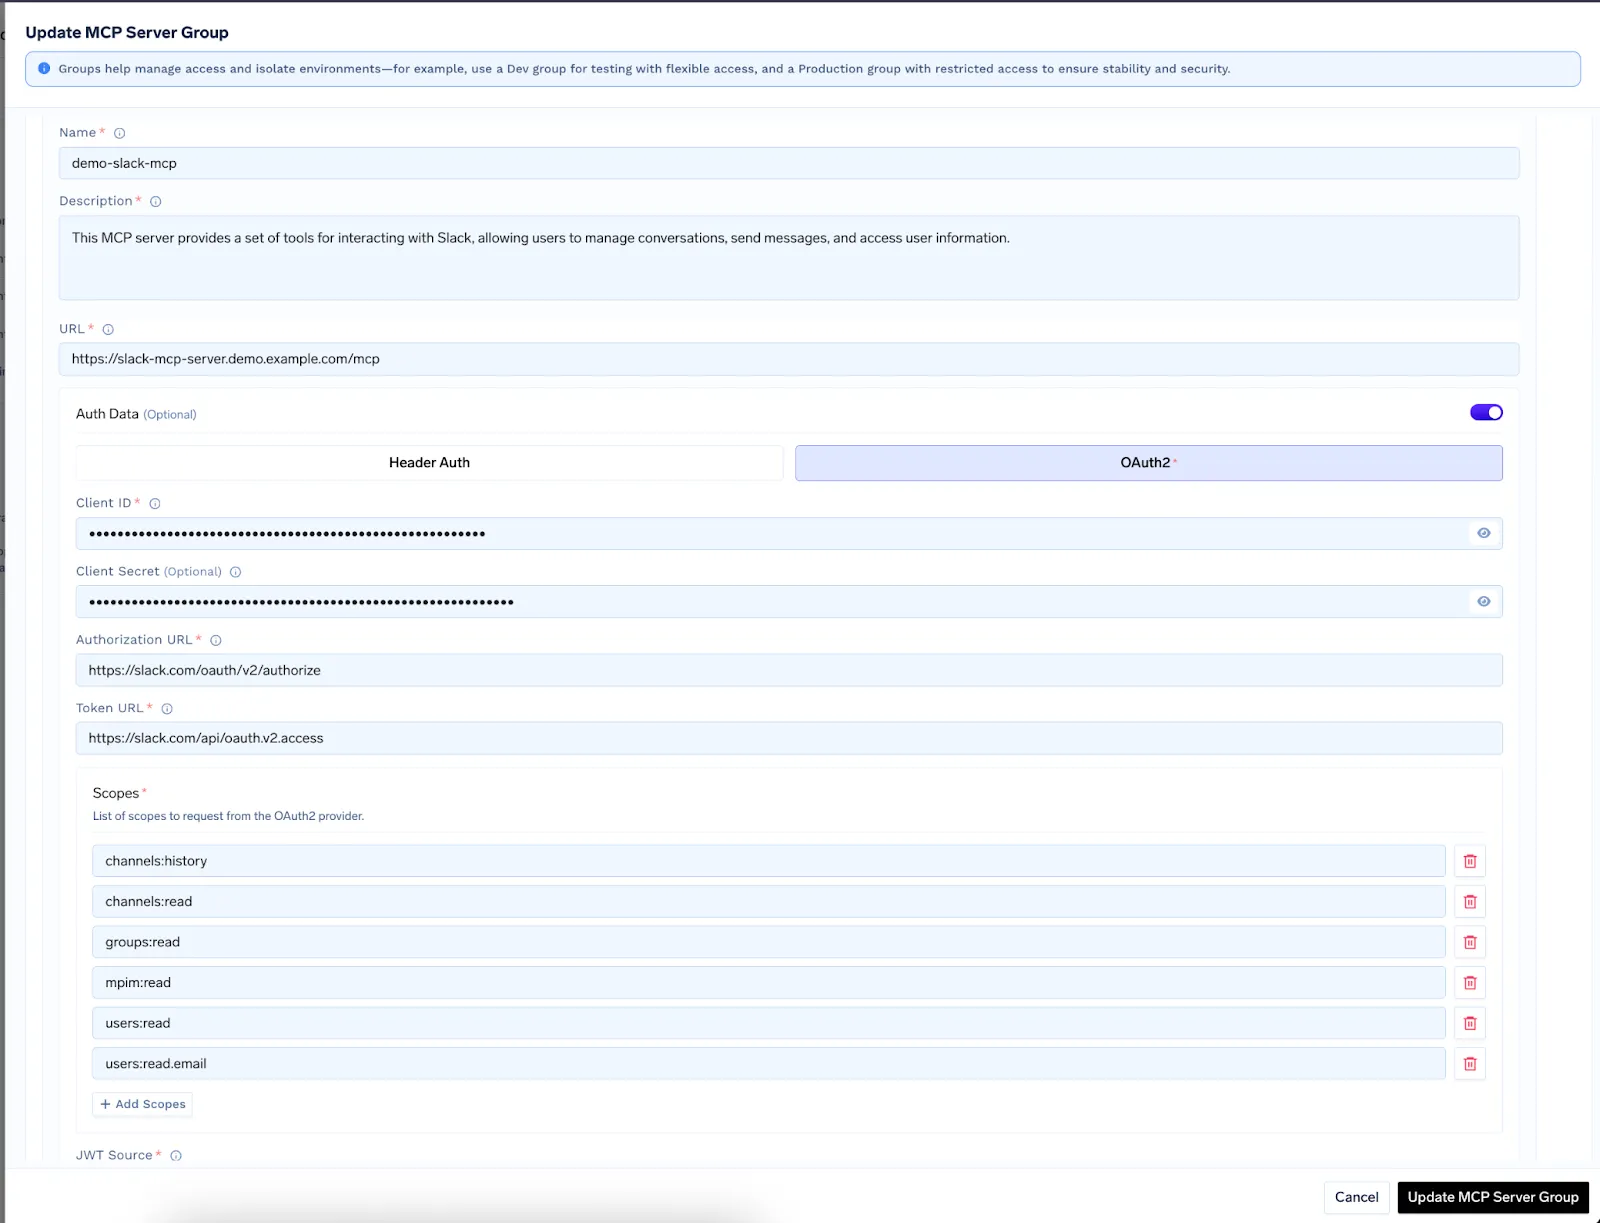
The Gateway supports multiple authentication schemes, including no authentication, header-based tokens, and OAuth2 client credentials, with federated SSO via identity providers such as Okta and Azure AD. OAuth2 credentials are stored securely in TrueFoundry’s built-in secrets manager and injected automatically on proxy requests, centralizing credential management and reducing risk.

Developers can programmatically interact with registered MCP Servers using the official Python and TypeScript SDKs, which handle MCP authorization end-to-end, or via the AI Gateway Playground, an intuitive interface where you add MCP Servers, select tools, and run natural language prompts that invoke remote services in real time. Both the Playground and SDK provide “API Code Snippet” buttons to generate ready-to-use integration boilerplate in your preferred language.
TrueFoundry’s AI Gateway embeds enterprise-grade observability and load balancing. Requests are routed based on weight or latency to the healthiest endpoints, while all MCP invocations are trace-logged and audited in governance dashboards, ensuring compliance and performance monitoring. In a recent blog, the team describes how the Gateway acts as the central control plane for modern generative AI infrastructure, unifying LLMs, MCP Servers, and agent-to-agent protocols under one interface for low latency, high reliability, and seamless scalability. This approach empowers natural language orchestration across enterprise systems, enabling end-to-end automation—such as creating Jira issues from Slack alerts—without writing integration code.
MCP is not just another integration layer; it is the core infrastructure for the future of AI. As models evolve into agents that need to reason, act, and interact with tools, the demand for secure, modular, and scalable access becomes critical. Function calling helped start this journey, but it falls short at scale.
MCP solves this with a clean host, client, and server architecture, enabling dynamic tool discovery, structured invocation, and runtime flexibility. It turns scattered integrations into a unified, extensible ecosystem. Whether you're building agents, assistants, or automation pipelines, MCP provides the foundation for real-world utility. It brings structure and security to AI workflows, allowing teams to build confidently, without compromise.
Struggling to manage MCP connections at scale? TrueFoundry’s MCP Gateway gives you the control and observability you need. Book a demo now.
TrueFoundry AI Gateway delivers ~3–4 ms latency, handles 350+ RPS on 1 vCPU, scales horizontally with ease, and is production-ready, while LiteLLM suffers from high latency, struggles beyond moderate RPS, lacks built-in scaling, and is best for light or prototype workloads.






The latest news, articles, and resources sent to your inbox